Cybersecurity researchers have uncovered two critical vulnerabilities in PHP, a programming language used by millions of websites worldwide, prompting security warnings and emergency updates across several countries.
The flaws, which had reportedly existed in the software for years, were identified through research involving artificial intelligence tools. Cybersecurity companies Wiz and Calif worked with OpenAI on the “Patch the Planet” project, which focuses on finding weaknesses in widely used internet infrastructure.
Wiz estimates that approximately 70 per cent of the internet could be affected by the vulnerabilities because of PHP’s widespread use.
The discovery has prompted website operators and government agencies to review their systems after developers released a software update on Wednesday to address the flaws.
Thai Duong, chief of Calif, told the Daily Mail that ordinary internet users had limited ability to address the issue themselves.
“The reality is that there’s very little the average internet user can do,” Duong said. “Should they be concerned? Yes, but there’s no need to panic. The responsibility lies with website operators, hosting providers and the broader security community.”
What Is PHP and Why Is It So Widely Used?
PHP, which stands for Hypertext Preprocessor, is an open-source programming language used to build and operate websites.
It is a server-side technology that allows websites to communicate with databases and process information before presenting it to visitors. The software supports functions such as online shopping, account management and digital forms.
PHP became widely used in the early 2000s, and its role in popular websites has made it an important part of the internet’s underlying infrastructure.
Because the language is free and open-source, it is used across a wide range of organisations, including businesses, universities and government institutions.
Websites that do not directly rely on PHP may also be exposed through third-party software, extensions or plugins that use it.
Duong said PHP’s early success helped establish it throughout the online ecosystem, with many widely used applications built around the language.
The widespread adoption of PHP means that a vulnerability in the software can affect organisations that may not immediately realise their systems depend on it.
How the PHP Vulnerabilities Could Be Exploited
The vulnerabilities have been described as critical because they could allow attackers to execute code remotely on affected systems.
In practical terms, an attacker could potentially gain control of a vulnerable website or server without first obtaining a legitimate user’s password.
Once inside a compromised system, criminals could steal sensitive information, change website content, interrupt services or use the affected server to access other parts of an organisation’s internal network.
Other potential consequences include installing malware, impersonating legitimate websites, locking administrators out of their systems and accessing private data stored on affected servers.
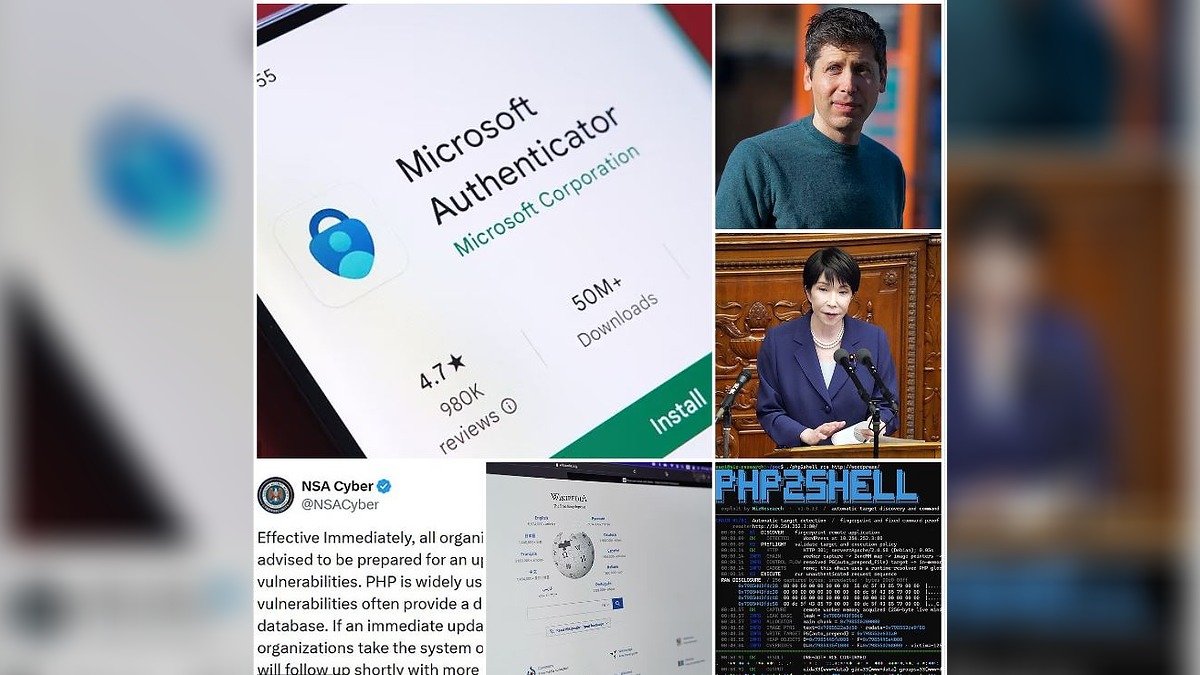
The vulnerabilities have been associated with the name “PHP2Shell”.
Professor Richard Buckland of the University of New South Wales said PHP developers had been aware of the weakness for some time, but had initially struggled to establish how attackers could exploit it.
He said concern about the issue had increased around two years ago, although developers had not initially considered it urgent because the practical method of exploiting the weakness was unclear.
OpenAI and Cybersecurity Firms Identify the Flaws
The discovery was made through the “Patch the Planet” initiative, which brought together Calif, Wiz and OpenAI to identify weaknesses in widely used software.
OpenAI said Calif used its GPT-5.6 Sol model to identify two critical PHP vulnerabilities, while Wiz independently discovered and verified the same flaws.
In a blog post, OpenAI described the findings as one of the most significant security issues in recent memory.
Wiz said artificial intelligence had helped researchers understand weaknesses in code that had existed for more than a decade and develop a working exploit.
The findings have also raised concerns about how artificial intelligence could change the process of discovering and exploiting software vulnerabilities, particularly when technical details become publicly available.
Governments and Major Websites Move to Reduce Risk
PHP developers released an update on Wednesday to address the two vulnerabilities, leaving website owners and operators responsible for applying the fixes to their systems.
The United Kingdom’s National Cyber Security Centre urged organisations using PHP to install the updated software.
“Organisations using any version of PHP are affected, and all organisations are highly encouraged to update to the latest fixed version,” the agency said.
The United States National Security Agency also advised organisations to prepare for the update. It said systems should be taken offline if an immediate update was not possible and the vulnerability could not otherwise be mitigated.
Japan’s Prime Minister, Sanae Takaichi, urged people to take action to protect their websites, saying temporary suspension could be considered where applying the fix promptly was difficult.
Several organisations have already taken systems offline as a precaution.
The Wikimedia Foundation, which operates Wikipedia, temporarily shut down a number of systems. The BBC also took offline websites hosting programmes including Doctor Who and The Traitors.
Public organisations in Scotland, including councils and health boards, were among those reported to have taken websites offline. Government and public-sector systems in Finland, Australia and the Netherlands were also reported to have been affected by precautionary shutdowns.
In the Netherlands, the measures included the Dutch Parliament’s website, the national cybersecurity agency’s website and the public-facing website of the Port of Rotterdam.
Security Experts Report a Surge in Exploitation Attempts
Although the full extent of any successful attacks remains unclear, cybersecurity companies have reported a sharp increase in attempts to exploit the vulnerabilities.
Matthew Prince, chief executive of Cloudflare, said the company had observed thousands of attempts across its network during the 10 hours before the issue was publicly announced.
According to Prince, the number increased to tens of thousands within 45 minutes of the announcement, reached hundreds of thousands within two hours and subsequently rose into the millions.
Dr Junade Ali, a cybersecurity expert at the Institution of Engineering and Technology, said the vulnerabilities were significant and that there was evidence they were already being exploited. He added that several firewall companies had introduced protections.
Amazon Web Services also reported exploitation attempts. The company said the vulnerability was being widely exploited and that it had encountered attacks as early as October 17, four days before the public disclosure.
Details of the flaw reportedly appeared on social media on Tuesday, followed by another attack against Amazon’s systems on October 21.
CJ Moses, chief information security officer at AWS, said one incident appeared to involve a threat actor, although it remained unclear how that actor had obtained information about the exploit before the vulnerability was publicly disclosed.
Researchers have not established how the information became available early. Experts have suggested that attackers may also have used artificial intelligence to identify or develop methods of exploiting the weakness.
AI Could Change How Software Vulnerabilities Are Disclosed
Dr Shaanan Cohney of the University of Melbourne said artificial intelligence was making it easier for attackers to identify vulnerabilities, even when only limited information about a flaw had been released publicly.
He explained that security researchers previously had more time between the announcement of a potential vulnerability and the discovery of a practical method for exploiting it.
According to Cohney, AI tools have shortened that window, creating challenges for organisations responsible for disclosing security flaws and giving users time to install fixes.
The PHP incident has therefore raised questions about how software vulnerabilities should be announced and managed when attackers may be able to use automated tools to develop exploits quickly.
What Website Owners Should Do
Website operators have been urged to install the latest fixed version of PHP and check that all systems relying on the software are protected.
Businesses should consult their IT teams and hosting providers to confirm that updates have been applied across their websites, servers, plugins and other connected components.
Experts have warned that applying the main PHP update may not be sufficient if a website relies on third-party tools or extensions that remain vulnerable.
Because websites often combine multiple software components, a weakness in one unpatched element could leave a wider system exposed. Some operators may also be unaware that PHP is running within their infrastructure.
Organisations unable to apply the fix immediately have been advised to consider taking vulnerable systems offline until adequate protection is in place.
Advice for Ordinary Internet Users
Cybersecurity experts say most ordinary internet users cannot directly fix the PHP vulnerabilities, as the responsibility rests primarily with the organisations operating affected websites.
However, users can take steps to reduce the amount of information exposed if an online service is compromised.
Jake Moore, global cybersecurity adviser at ESET, recommended that people use multi-factor authentication, passkeys and digital payment services where available.
He also advised online shoppers to consider guest checkout options rather than creating accounts that store additional personal information and payment details.
Users should avoid suspicious websites, limit the sensitive information they provide online and follow updates from official government cybersecurity agencies.
Professor Buckland also warned that compromised websites could potentially display altered or misleading information if attackers gained control of their content.
He advised people to be cautious about information published on websites in the coming days and to rely on announcements from government agencies and trusted organisations while the vulnerabilities are being addressed.
Extent of the Damage Remains Unclear
Despite reports of widespread exploitation attempts and precautionary shutdowns, it remains unclear how many websites have been successfully compromised or whether personal data has been stolen as a result of the PHP vulnerabilities.
Security companies and website operators continue to assess the risks as updates are deployed.
Experts have warned that the coming weeks could bring further attempts to exploit vulnerable systems as more information about the flaws becomes available.
The immediate priority remains ensuring that affected websites are updated, connected software components are checked and systems that cannot yet be secured are protected against potential attacks.
